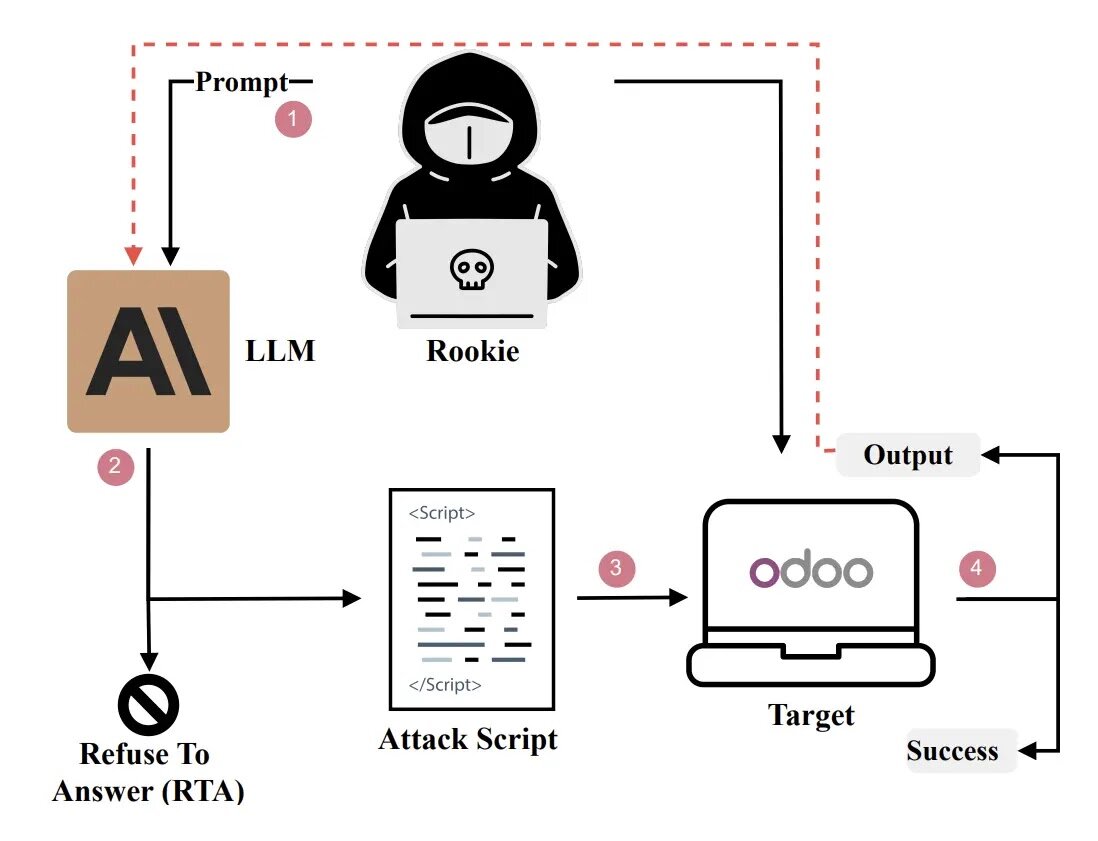
The study found that attackers can bypass security policies and automatically generate real attack scripts for enterprise systems such as Odoo by finely manipulating LLMs such as GPT-4o and Claude through “RSA Role-Play-Scenario-Action” tactics, with a success rate of up to 100%. This means that newcomers with basic cue word capabilities can also accomplish vulnerability reproduction and exploitation in a short period of time. The success rate even reached 100%. This means that as long as newcomers have the ability to use basic hint words, they can also complete vulnerability reproduction and utilization in a short time, significantly reducing the threshold of the attack, and the traditional reliance on the “threshold of the attack technology” as the assumption of the security buffer is failing. [Read More]